


Rösti Threat Intel
Check IOCs against public threat-intelligence reports and search reports, YARA rules, MITRE ATT&CK techniques and CVEs from rosti.dev.
 View in the Claude registry
- Brand
- Unknown
- Category
- Pending
- Primary Subcategory
- Threat Detection & SIEM/XDR Monitoring
Integration details
Description
Rösti (rosti.dev) collects public threat-intelligence reports from security vendors, researchers and CERTs, and extracts their indicators of compromise (IOCs), YARA rules, MITRE ATT&CK techniques and CVEs. This connector brings that data into Claude. Ask Claude whether IPs, domains, URLs, hashes or email addresses appear in any report, paste up to 1,000 indicators at once, or have it read a report's IOCs and YARA rules. Claude can find reports by keyword, source, CVE, ATT&CK technique or date, show which reports share infrastructure, and give you a download link for a report export in formats such as STIX or MISP. Defanged values like hxxps://evil[.]com are accepted. Every IOC comes with its type, tags, the report it was found in and a link to the original publication, plus Rösti's false-positive risk, which flags values such as popular domains that also carry benign traffic. The connector is free and read-only. It works without an account on a shared quota; signing in with a free Rösti account gives you your own quota.
- Integration type
- Connector
- Verification status
 Community connector
- Platform
- Claude
- Category
- Pending
- Primary Subcategory
- Threat Detection & SIEM/XDR Monitoring
- Secondary Subcategories
- None listed
- Brand
- Unknown
- Access
- No account required
- First tracked
- 2026-11-04
- Tool count
- 11
- Market
- US
The broad Category that contains the Primary Subcategory.
The Primary Subcategory used for this profile’s headline score.
Other Subcategories where the Integration is listed.
 Agent DiscoverabilityClaude Discoverability Score
Claude Connector discovery is coming soon
Community Connectors only appear in Claude’s registry.Once verified, organic discovery begins and we can calculate your score.Read more about Community Connector verification.
No spam. Unsubscribe any time.
What discovery looks like
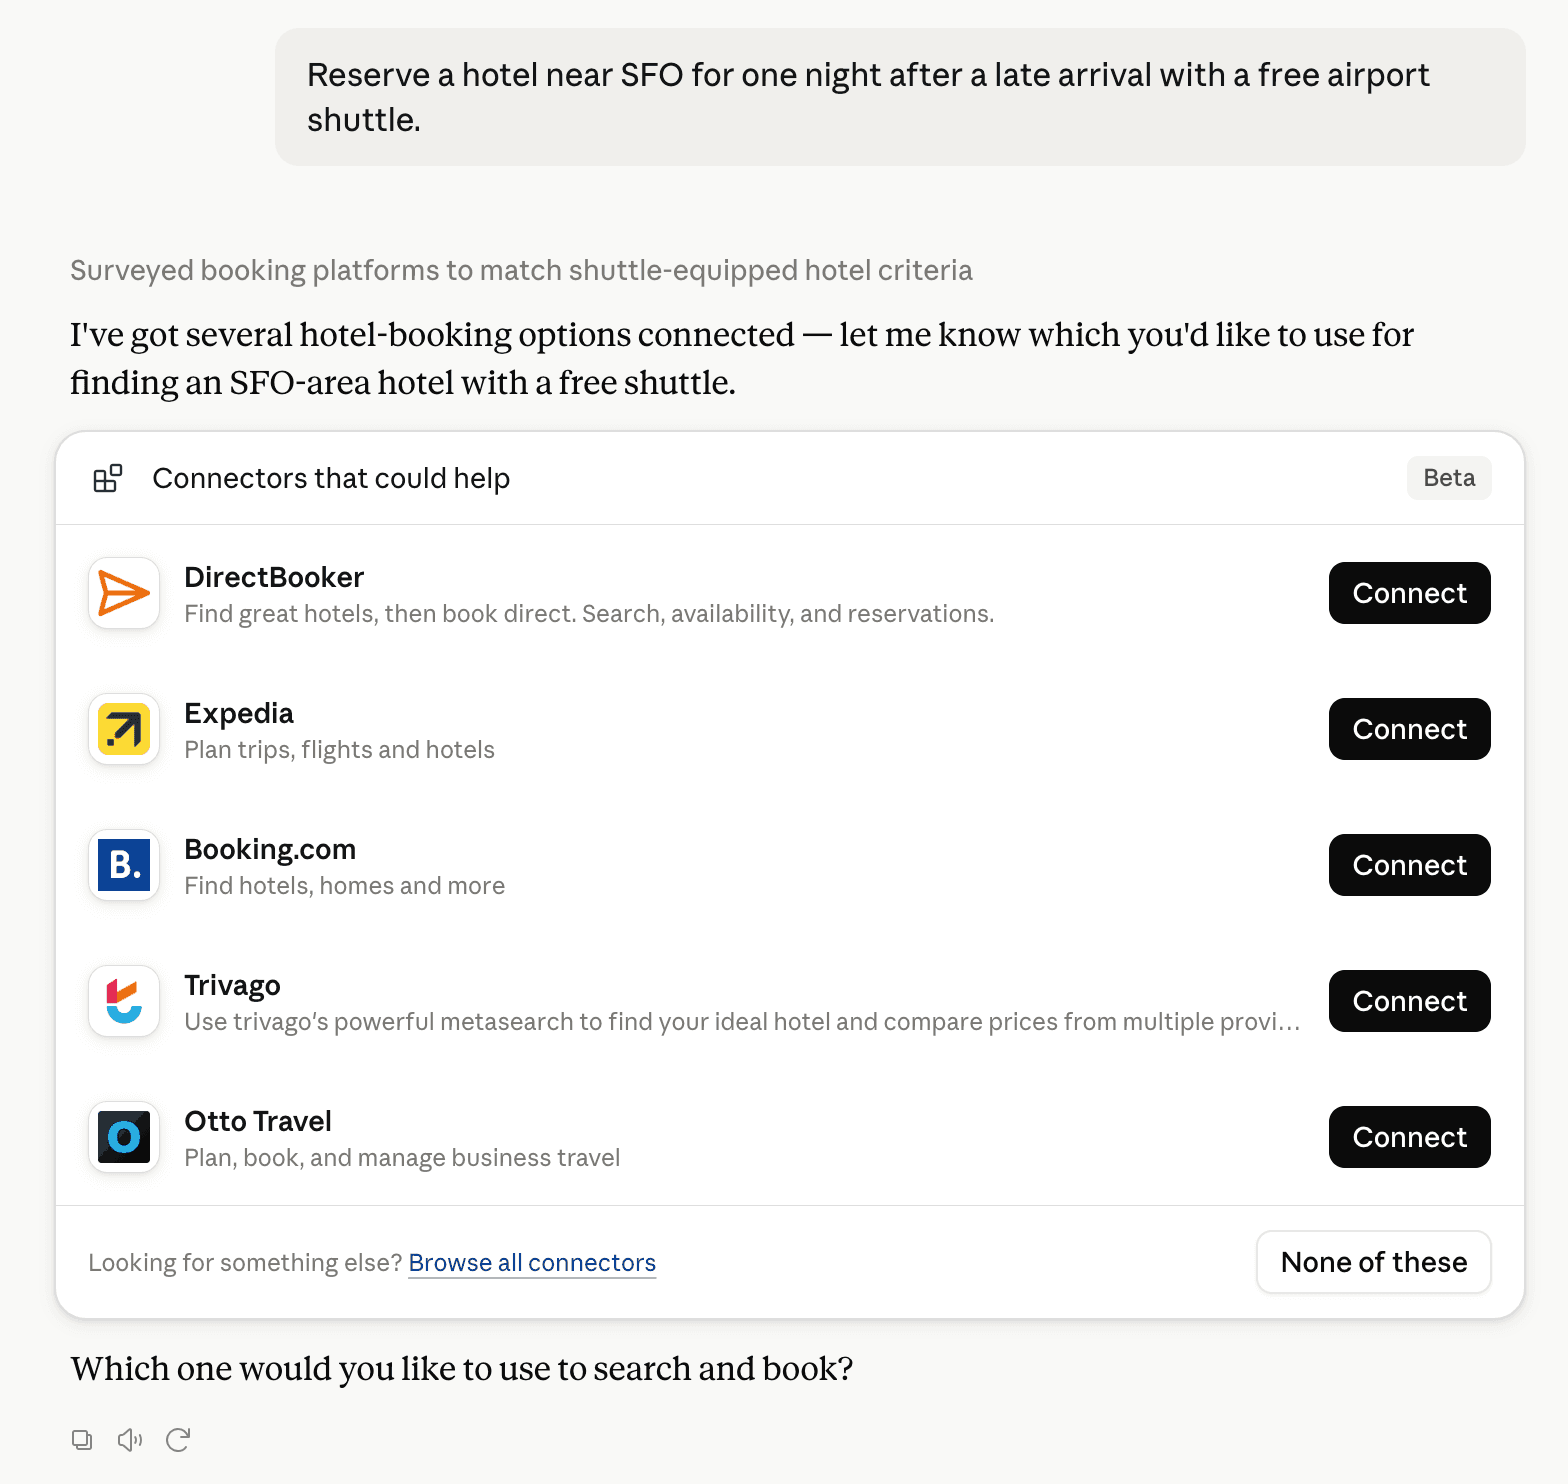
Claude can surface verified Connectors when they match a user’s Prompt.
How Claude Connector discovery works
Your Connector will compete to appear for users’ Prompts once Claude verifies it
Competing in Claude Threat Detection & SIEM/XDR Monitoring
View Category11 tools agents can invoke

Rösti Threat Intel Claude Connector FAQ
How the directory, categories and Discoverability Score work.
Read the methodologyHow do I improve Rösti Threat Intel's Claude Connector discoverability?
The levers are the listing surface agents actually read: names, descriptions, keywords, tool metadata, and registry health. Which lever matters depends on where discovery breaks, which is what continuous measurement shows.
What are Rösti Threat Intel alternatives on Claude?
As of 2026-11-05, Rösti Threat Intel competes with Anvilogic, Brandefense Atlas, Brandefense MCP, DarkWebSonar, DugganUSA Threat Intelligence, ELLIO, Exaforce, Fingerprint and 12 more in Claude Threat Detection & SIEM/XDR Monitoring, ranked by public Discoverability Score.
Where is this profile measured?
This profile uses the geography attached to the latest public registry snapshot: US. Locale tags are intentionally omitted.