
DepScout
Check npm, PyPI, Go, Maven, crates.io and NuGet packages and whole lockfiles, including transitive dependencies, for known vulnerabilities and malware, and find the minimum safe version.
 View in the Claude registry
- Brand
- DepScout
- Category
- Developer Tools
- Primary Subcategory
- Application Security & Vulnerability Management
Integration details
Description
DepScout checks open-source packages against live vulnerability and malware data, so answers about whether a package is safe, and which version to use, come from current advisories instead of model memory. What it does: - Checks one package (npm, PyPI, Go, Maven, crates.io or NuGet) at a given version or its latest release. It flags malicious packages and compromised releases first, then lists known vulnerabilities with severity, CVE IDs and the version that fixes each one, plus the minimum version that clears them all. - Reports the latest stable version, whether a version is outdated or deprecated, the last release date, licences, and the source repository's OpenSSF Scorecard. - Audits a whole lockfile in one call, including transitive dependencies: package-lock.json, yarn.lock, pnpm-lock.yaml, requirements.txt, poetry.lock, uv.lock, Pipfile.lock, Cargo.lock, go.sum, go.mod, packages.lock.json or gradle.lockfile (up to 3,000 packages). Only the packages with problems come back, each with an upgrade target. - Checks a short list of pinned dependencies (up to 50) when you don't have the lockfile. - Explains a single advisory by ID (CVE, GHSA, PYSEC, GO, RUSTSEC or MAL): severity, affected and fixed version ranges, and references. - Ready-made prompts: "Audit my dependencies", "Is this package safe?" and "Explain a CVE". Who it's for: developers using Claude, Claude Code or other AI assistants who want to vet a dependency before installing it, audit a project's lockfile, or pick a safe version. Limitations: data comes from OSV.dev and deps.dev. A clean result means no known advisory for that exact version, not a guarantee of safety, and newly published malware may not be listed yet. A plain package list or package.json covers only the packages named in it; a lockfile covers transitive dependencies. DepScout is read-only, does not store the files you send, and is not affiliated with OSV.dev, deps.dev, Google, the OpenSSF, GitHub or any package registry.
- Integration type
- Connector
- Verification status
 Community connector
- Platform
- Claude
- Primary Subcategory
- Application Security & Vulnerability Management
- Secondary Subcategories
- None listed
- Brand
- DepScout
- Access
- No account required
- First tracked
- 2026-10-02
- Tool count
- 4
- Market
- US
The Primary Subcategory used for this profile’s headline score.
Other Subcategories where the Integration is listed.
 Agent DiscoverabilityClaude Discoverability Score
Claude Connector discovery is coming soon
Community Connectors only appear in Claude’s registry.Once verified, organic discovery begins and we can calculate your score.Read more about Community Connector verification.
No spam. Unsubscribe any time.
What discovery looks like
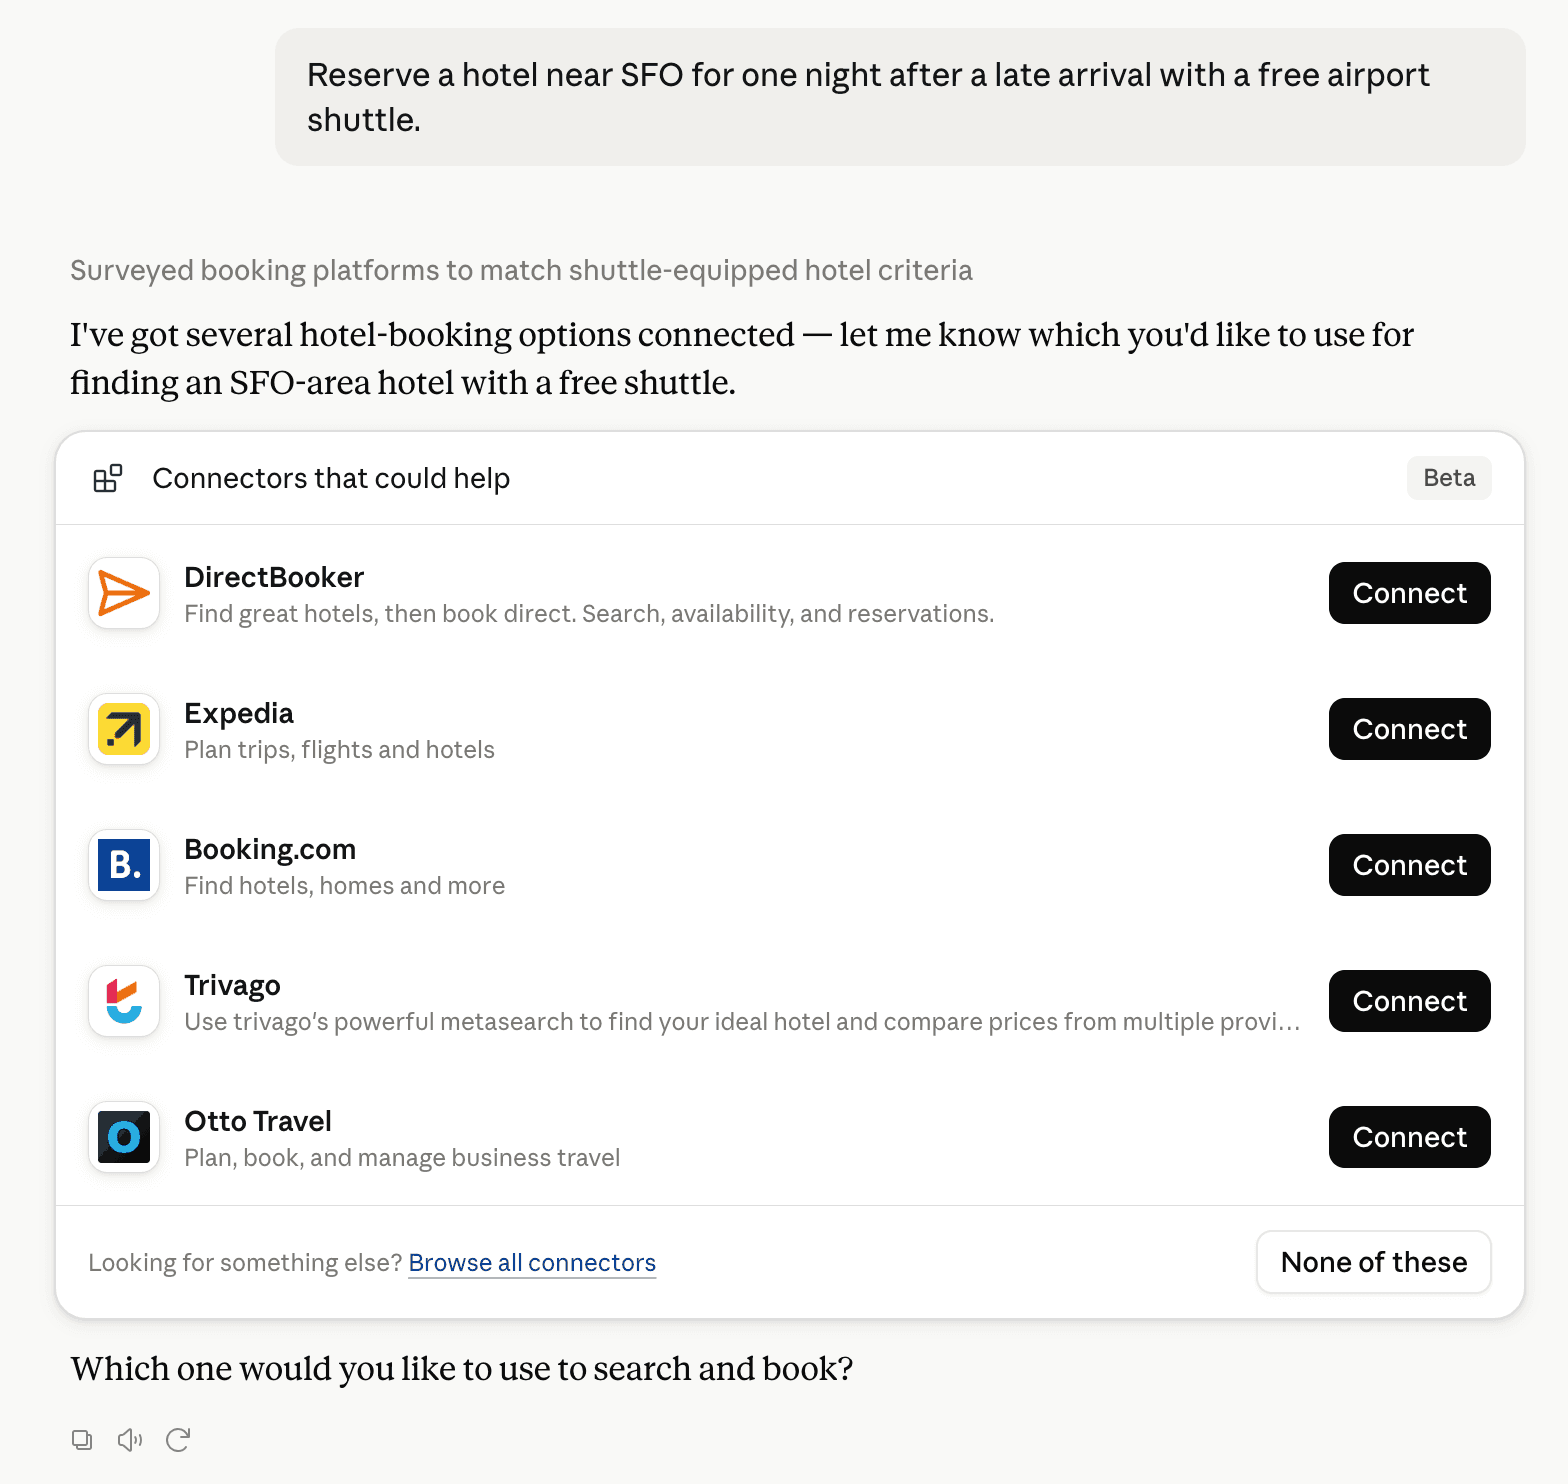
Claude can surface verified Connectors when they match a user’s Prompt.
How Claude Connector discovery works
Your Connector will compete to appear for users’ Prompts once Claude verifies it
Competing in Claude Application Security & Vulnerability Management
View Category4 tools agents can invoke

DepScout Claude Connector FAQ
How the directory, categories and Discoverability Score work.
Read the methodologyHow do I improve DepScout's Claude Connector discoverability?
The levers are the listing surface agents actually read: names, descriptions, keywords, tool metadata, and registry health. Which lever matters depends on where discovery breaks, which is what continuous measurement shows.
What are DepScout alternatives on Claude?
As of 2026-11-02, DepScout competes with CloudBees Unify MCP Server, ActiveLayer, Affirmed AI, AgentAvow, AgentMart Site Check, AI Website Security, Apiiro Guardian, Arcjet and 33 more in Claude Application Security & Vulnerability Management, ranked by public Discoverability Score.
Where is this profile measured?
This profile uses the geography attached to the latest public registry snapshot: US. Locale tags are intentionally omitted.