
SystemAudit
Scan any public GitHub repository for security risks, structure and exposed credentials — a health score and plain-English findings, no sign-in.
 View in the Claude registry
- Brand
- SystemAudit
- Category
- Developer Tools
- Primary Subcategory
- Application Security & Vulnerability Management
Integration details
Description
Ask Claude "Should I depend on github.com/lukeed/clsx?", "Compare these two libraries" or "Give me a due-diligence read of this repo". SystemAudit gives a security and code-health review of any public GitHub repository: a health score out of 100, the top risks in plain English, how the project is built, and how many potential hardcoded credentials it contains. Works on any public repository, with no sign-in and no account. Private repositories are refused by design: the connector holds no GitHub account access, which keeps it safe to point at any public repository. Scan private ones on systemaudit.dev. Built for the moment before you commit to a codebase: choosing an open-source dependency, running technical due diligence on an investment or acquisition, inheriting a repository, or sanity-checking code an AI tool generated. Three tools: scan_repository: health score, ranked risks, how the project is built, credential counts, and how many files were read out of how many exist. get_architecture: package ecosystem, architecture pattern, language mix, dependency count, circular imports and files nothing else imports. secrets_summary: potential hardcoded credentials and committed environment files, counted by severity. Honest by design. Every answer states how many files were read, so a clean result is never mistaken for a clean repository. The connector returns credential counts by severity only, never a file, line or value; the linked full report on systemaudit.dev shows locations for critical and high findings, as it does for any public repository scan. Your conversation stays yours: the connector receives only the repository you name. No code is executed, no file contents are returned, and we keep the resulting report, not a copy of the repository. Response times: an already-scanned repository answers from its saved result. A first scan reads the repository through the GitHub API, so larger repositories take longer. New scans are rate-limited.
- Integration type
- Connector
- Verification status
 Community connector
- Platform
- Claude
- Primary Subcategory
- Application Security & Vulnerability Management
- Secondary Subcategories
- None listed
- Brand
- SystemAudit
- Access
- No account required
- First tracked
- 2026-09-27
- Tool count
- 3
- Market
- US
The Primary Subcategory used for this profile’s headline score.
Other Subcategories where the Integration is listed.
 Agent DiscoverabilityClaude Discoverability Score
Claude Connector discovery is coming soon
Community Connectors only appear in Claude’s registry.Once verified, organic discovery begins and we can calculate your score.Read more about Community Connector verification.
No spam. Unsubscribe any time.
What discovery looks like
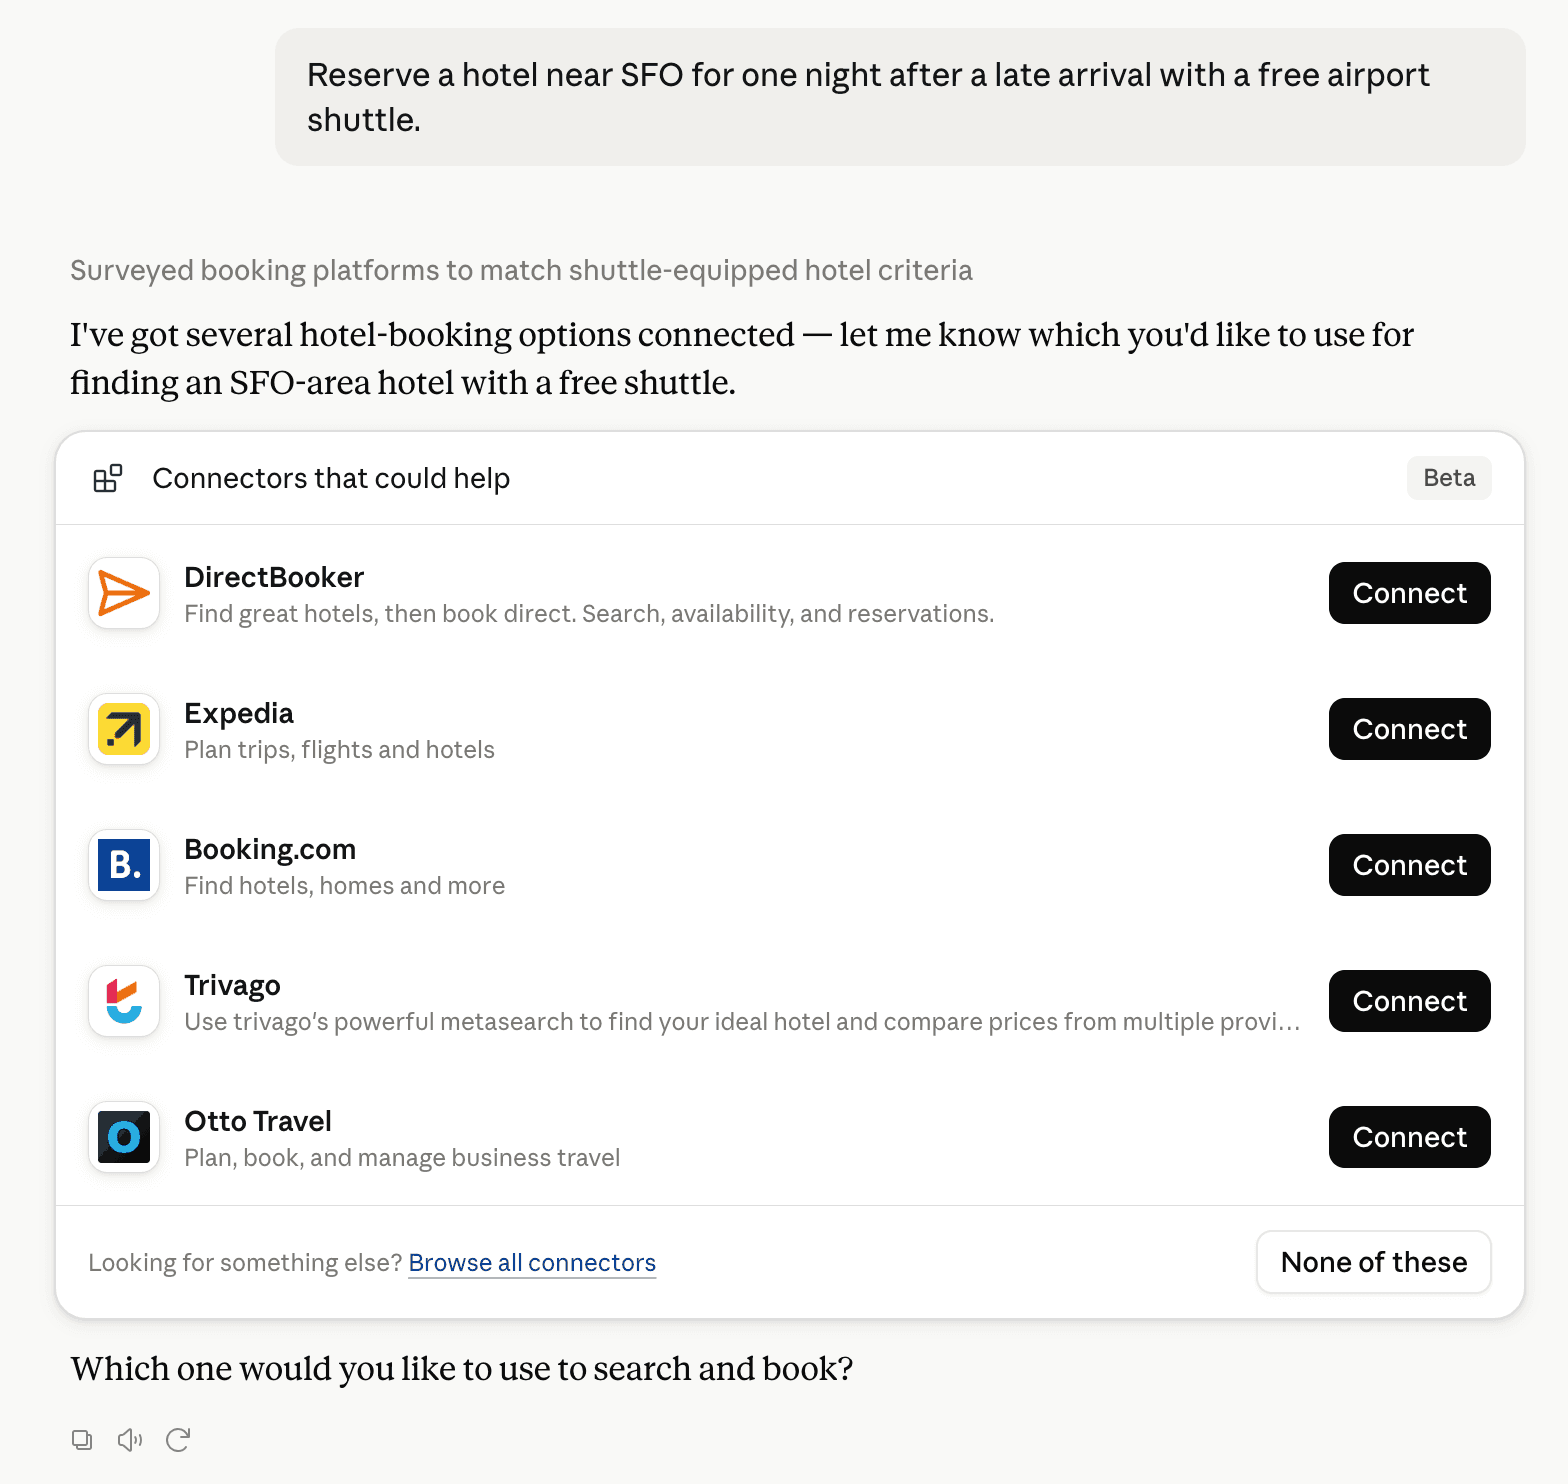
Claude can surface verified Connectors when they match a user’s Prompt.
How Claude Connector discovery works
Your Connector will compete to appear for users’ Prompts once Claude verifies it
Competing in Claude Application Security & Vulnerability Management
View Category3 tools agents can invoke

SystemAudit Claude Connector FAQ
How the directory, categories and Discoverability Score work.
Read the methodologyHow do I improve SystemAudit's Claude Connector discoverability?
The levers are the listing surface agents actually read: names, descriptions, keywords, tool metadata, and registry health. Which lever matters depends on where discovery breaks, which is what continuous measurement shows.
What are SystemAudit alternatives on Claude?
As of 2026-11-02, SystemAudit competes with CloudBees Unify MCP Server, ActiveLayer, Affirmed AI, AgentAvow, AgentMart Site Check, AI Website Security, Apiiro Guardian, Arcjet and 33 more in Claude Application Security & Vulnerability Management, ranked by public Discoverability Score.
Where is this profile measured?
This profile uses the geography attached to the latest public registry snapshot: US. Locale tags are intentionally omitted.